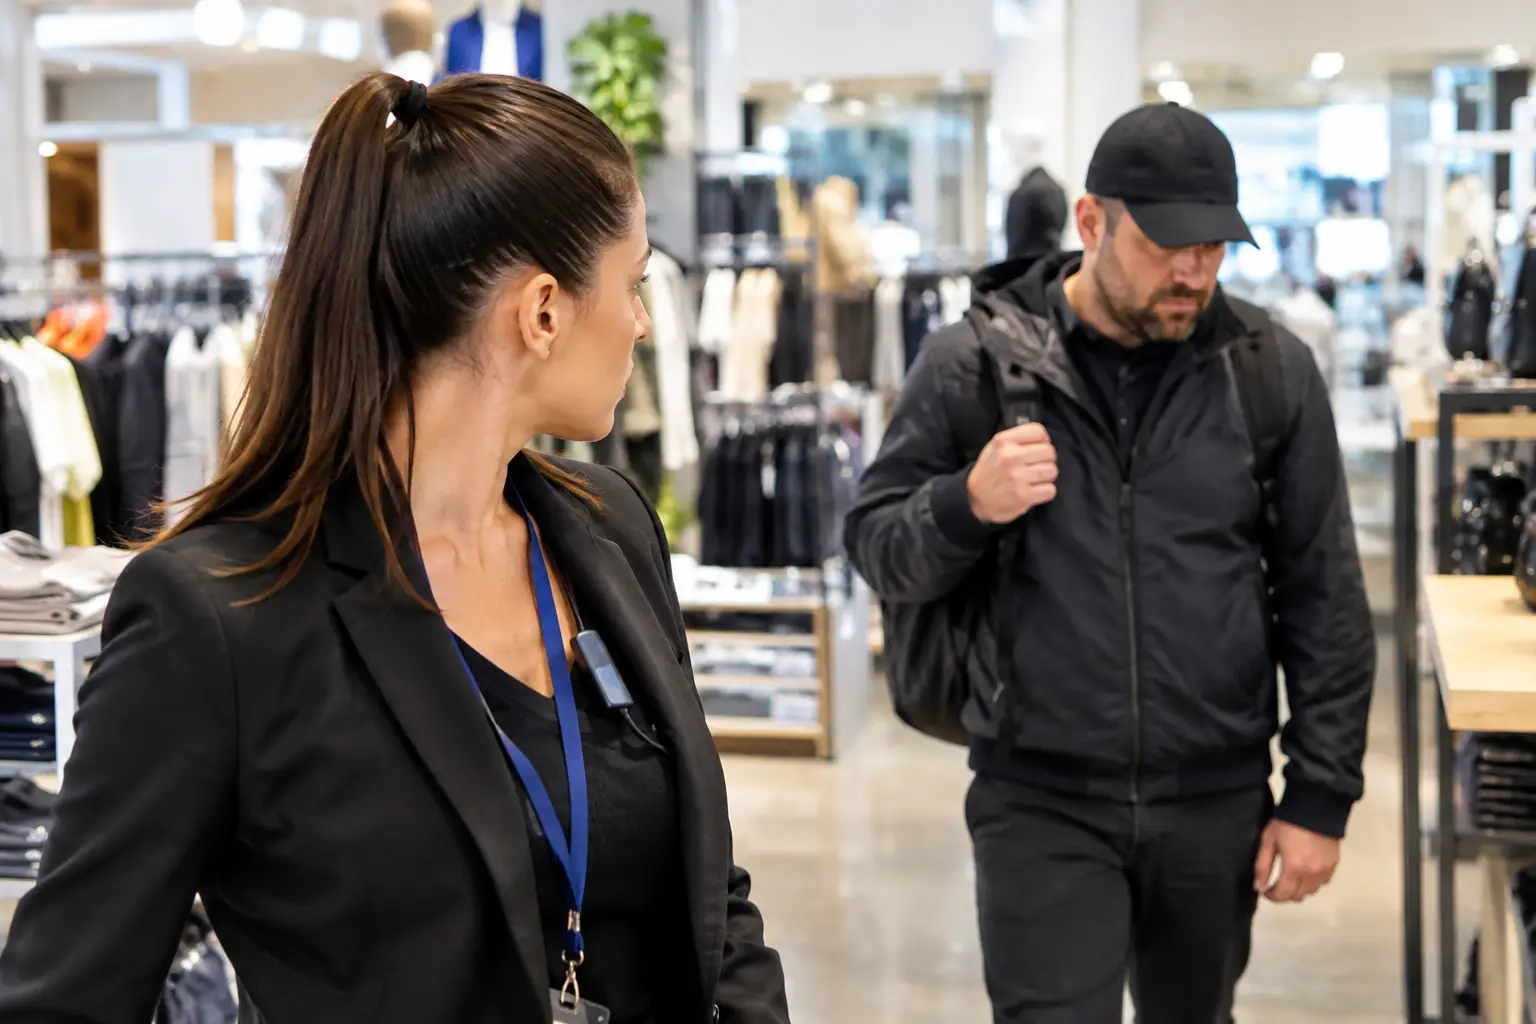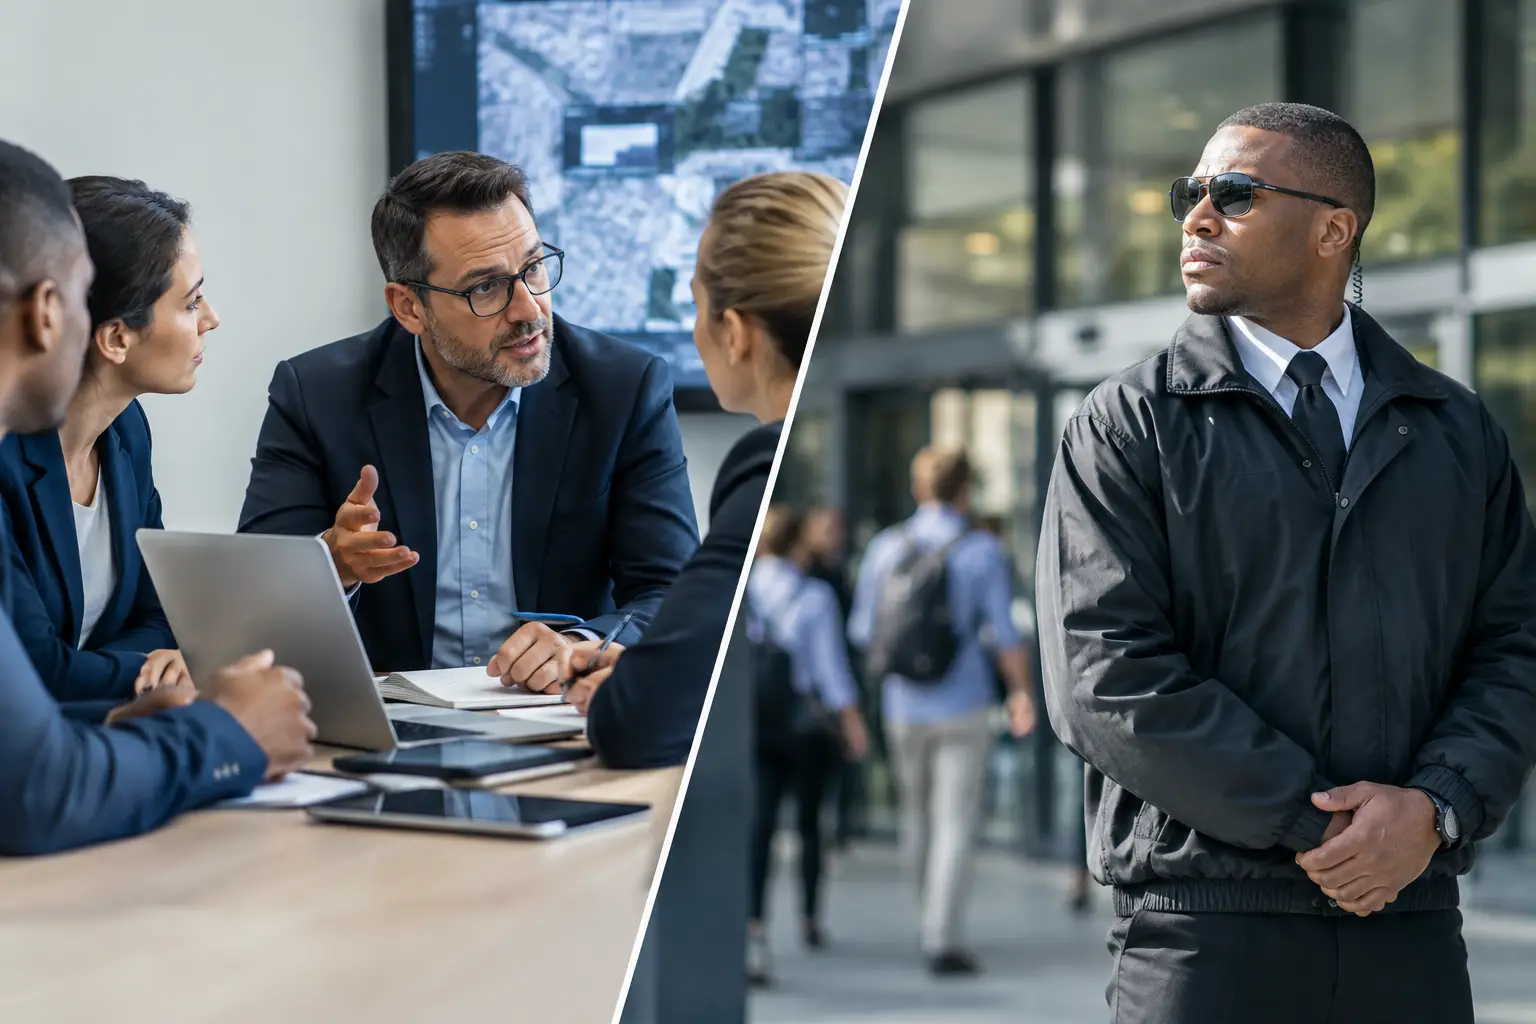
A control room full of screens can look impressive while the people responsible for security still lack the information, authority or confidence to act. That is the central problem with much security technology. Organisations buy systems to demonstrate that risk is being addressed, then discover during an incident that alerts are unclear, ownership is uncertain and response plans have never been properly tested.
Technology has a vital place in protective security. It can extend awareness, support early intervention, record evidence and help teams coordinate under pressure. But it does not make an organisation capable by itself. Capability comes from the relationship between the system, the people using it, the decisions they are expected to make and the operational conditions they face.
The uncomfortable reality is that more technology can create more noise. If a security team cannot distinguish a meaningful alert from routine activity, the system has increased workload without necessarily reducing risk. If an access control system is routinely bypassed because it disrupts operations, the weakness is not simply user behaviour. It may be a design failure.
Security technology is not a security strategy
CCTV, access control, intruder detection, visitor management, communications platforms and security management software all have legitimate uses. Each can contribute to prevention, detection, delay, response or recovery. None replaces a clear understanding of the threats that matter to a particular site, service or organisation.
A transport environment, public venue, corporate office and construction project may all use cameras. Their security requirements will be very different. A venue may need staff to recognise concerning behaviour and communicate quickly with supervisors. A corporate site may need tighter control of visitors, contractors and sensitive areas. A construction project may be more exposed to changing site boundaries, temporary access arrangements and inconsistent supervision.
The starting point is therefore not a product catalogue. It is a threat, vulnerability and risk assessment that asks practical questions. What are we trying to protect? What could realistically go wrong? Where are the points of exposure? What decision must someone make when an alert is raised? What action is possible within the time available?
Without those answers, organisations tend to buy generic solutions and call the result a strategy. It rarely is. A strategy makes choices about priorities, resources, tolerable risk and responsibilities. Technology should support those choices, not substitute for them.
Design security technology around decisions
A useful system changes a decision for the better. It gives the right person relevant information early enough to take proportionate action. That principle sounds obvious, yet it is often missing from procurement discussions.
Consider a camera system installed to improve situational awareness. The practical questions are not limited to image quality, coverage or storage. Who monitors it? At what times? What behaviours or events require attention? How will an operator alert colleagues? Who can make a decision to investigate, restrict access, escalate or stand down? What happens if the operator is dealing with several demands at once?
If those questions are left unanswered, cameras may record an event without improving the organisation’s ability to manage it. Recording after the fact has value, but it is not the same as active protection.
The same principle applies to access control. A system should reflect how people genuinely work. Staff, visitors, contractors, delivery personnel and emergency responders do not all move through a site in the same way. A design that ignores operational reality will soon attract workarounds. Doors get propped open. Passes are shared. Reception staff are asked to make exceptions they have not been trained or empowered to manage.
Good security design makes the secure action the workable action. It also accepts that some friction is necessary. The aim is not to remove every inconvenience. It is to ensure that the inconvenience is proportionate to the risk and understood by those affected.
Integration is useful only when it improves action
Integrated systems are often presented as an automatic improvement. A single platform that brings together video, alarms, access events and incident records can help a team understand what is happening. It can also create a complicated interface that staff use only at a basic level.
Integration is worthwhile when it shortens the path from detection to an informed decision. For example, linking an access event to nearby camera footage may help verify whether an issue needs attention. Bringing incident records into one place may reveal recurring weaknesses that would otherwise remain hidden.
It is less useful when it joins systems simply because they can be joined. Every connection introduces costs, training demands, support requirements and possible points of failure. The question is not whether integration is technically possible. It is whether it produces a meaningful operational advantage.
The human system decides whether the technology works
Most technology failures are not equipment failures. They are failures of ownership, training, supervision and judgement. A system may be installed correctly and still underperform because no one has defined normal use, exception handling or escalation.
This is particularly relevant where security teams operate under pressure. Alerts may arrive during busy periods, when staffing is thin or when information is incomplete. A person who has only been trained to use software menus is not necessarily prepared to assess relevance, communicate clearly and make a defensible decision.
Training should therefore go beyond product familiarisation. People need to understand the purpose of the system, its limitations and the decisions it supports. They need realistic scenarios that require them to interpret information, prioritise competing demands and work with operational colleagues. This is where generic completion certificates can be misleading. They may show attendance, but they do not demonstrate capability.
For counter terrorism preparedness, this distinction matters greatly. Technology may provide warning, support communication or help account for people, but staff still need to recognise when something requires escalation and know how to act within their role. The system is only one part of the protective security arrangement.
Test performance, not just installation
Commissioning is often treated as the end of a project. It should be the point at which proper assurance begins. A camera image may meet a technical specification, an alarm may activate and a door may lock. Those checks matter, but they do not prove that the whole security arrangement works under operational conditions.
Testing should examine the complete chain: detection, assessment, communication, decision, response and recording. It should include ordinary operating conditions as well as periods of pressure, such as shift changes, high visitor numbers, reduced staffing or simultaneous demands.
Exercises do not need to be theatrical to be valuable. A short, well designed scenario can expose whether messages reach the correct person, whether staff understand roles and whether a control room can support those on the ground. It can also reveal a common issue: teams may know how to report an event but not what information the receiving person needs to make a decision.
Findings must lead to action. If the same fault, blind spot or confusion appears repeatedly, it is not a minor observation. It is evidence that the organisation has accepted a known weakness. Technical adjustments may be needed, but so may clearer procedures, better supervision or a change in staffing arrangements.
Security technology needs an owner throughout its life
Security systems deteriorate operationally long before they fail technically. Changes in layouts, tenant arrangements, staffing, working practices and threat levels can make an original design less effective. A system installed five years ago may still function, while no longer serving the risk it was bought to address.
Every significant system needs clear ownership. That owner should understand its purpose, performance expectations, maintenance position, user issues and dependencies on other teams or suppliers. They should also have a route to challenge whether the system remains suitable.
This is particularly relevant as organisations prepare for duties associated with Martyn’s Law. The requirement should not be interpreted as an instruction to buy more equipment. The better question is whether current arrangements enable people to identify concerns, communicate, make decisions and respond effectively. In some cases, improved systems will be necessary. In others, the priority may be clearer roles, better training or more credible exercising.
Procurement should also account for the less visible costs. Licences, maintenance, replacement parts, cyber security, data management, training and contract oversight all affect long term value. The cheapest installation can become the most expensive option when it is difficult to support or abandoned after the initial project team leaves.
The right test for security technology is simple: when conditions become confused and time is limited, does it help your people make a better decision and take effective action? If the answer is uncertain, the gap is not just technical. It is a capability issue worth addressing before the system is needed most.